Introduction to Domain Names
A domain name is your business's unique online address, such as yourbusiness.com or yourcompany.co.uk. It is what customers type into their browser to find you, and what they recognise in email addresses, websites, and services.
More than a web link, a domain is part of brand identity. Think of it as a digital storefront: just as you would not let someone take over a physical office, domain names need to remain secure, accessible, and under organisational control.
Why Domain Management Matters
Proper domain management keeps the organisation's online presence secure and operational. Failing to manage domains properly can result in loss of website and email access, brand impersonation through lookalike websites, domain hijacking, traffic redirection, and reputational damage.
This guide sets out the main risks and the practical steps needed to manage domains coherently, with the same care given to other high-impact business assets.
Domain Risk Model
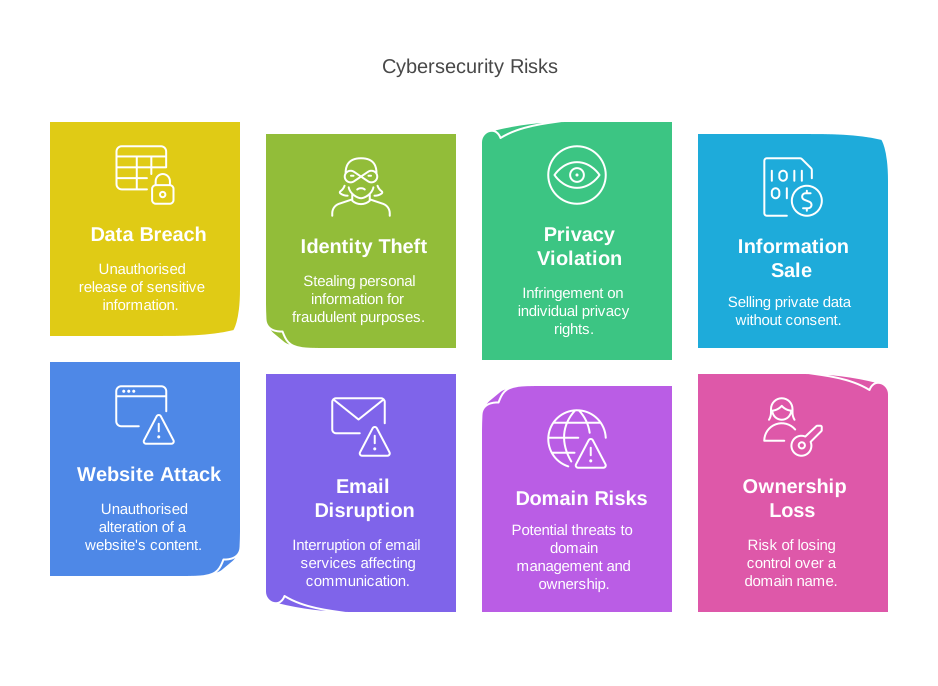
The domain model links common cybersecurity outcomes, such as data breach, identity theft, privacy violation, and information sale, to domain-specific risks such as website attack, email disruption, and ownership loss.
| Risk area | What it means | Primary control focus |
|---|---|---|
| Website attack | Unauthorised alteration, redirection, or misuse of a website's content or traffic. | Secure registrar access, DNS change control, monitoring, and recovery procedures. |
| Email disruption | MX record manipulation or domain loss can interrupt or intercept business email. | Protected DNS administration, strong authentication, and a tested email continuity plan. |
| Ownership loss | Weak records, stale contacts, or unauthorised transfers can cause loss of control over a domain. | Accurate registrant records, registrar locks, monitored contacts, and renewal governance. |
| Privacy and identity risks | WHOIS privacy, public contacts, phishing domains, and misleading certificates can affect trust and response. | Deliberate WHOIS policy, organisational contact details, impersonation monitoring, and appropriate certificates. |
What Good Looks Like
- Clear business ownership for every domain.
- Strong registrar account security, including multi-factor authentication.
- Documented renewal ownership and expiry monitoring.
- DNS records reviewed and kept current.
- Protection against lookalike domains and brand impersonation.
- Controlled change process for DNS and registrar changes.
- Separation of duties where domain administration is high impact.
Domain Management Risk Register
| Risk or issue | Description | Business impact | Mitigation strategies |
|---|---|---|---|
| Sale of Private Domain Information | Registrars may sell domain information marked as private, exposing sensitive data. | Unauthorised disclosure of information, privacy breaches, and potential legal implications. | Evaluate the need for domain privacy services and remove them where they create more risk than value. |
| Unauthorised Data Release to Authorities | Registrars may disclose private domain information to law enforcement or government agencies without adequate justification. | Unauthorised disclosure of information and potential damage to stakeholder trust. | Assess the value of domain privacy settings and confirm they provide a meaningful security advantage. |
| Loss of Domain Ownership Due to WHOIS Privacy | Domain ownership is determined by WHOIS records; privacy settings may obscure true ownership and complicate legal assertions. | Loss of domain control, operational disruption, financial loss, and reputational damage. | Ensure WHOIS records accurately reflect organisational ownership and support clear legal rights. |
| Privacy Hindering Intelligence Sharing | Private contact information in WHOIS records can prevent timely communication from security bodies about threats. | Delayed response to cyber threats and increased vulnerability to attack. | Include clear contact routes in WHOIS records and on public websites for incident reporting. |
| Denial and Theft of Email Services | Manipulation of MX records can allow attackers to intercept or disrupt email communications. | Privacy breaches, loss of productivity, and reputational harm. | Use strong authentication and access controls for domain management services, with a tested recovery plan. |
| Customer Identity Theft via Phishing | Domains redirected to fraudulent sites can lead to theft of customer credentials. | Reputational damage, regulatory fines, and loss of customer trust. | Secure domain management interfaces and maintain a well-defined incident response plan. |
| Traffic Inspection or Manipulation | Attackers may redirect domain traffic to malicious sites, capturing or altering data. | Information leakage, reputational damage, and potential legal consequences. | Protect domain control panels with strong authentication and validated recovery procedures. |
| Website Defacement | Redirecting domains to defamatory or malicious sites can damage brand image. | Reputational damage and loss of stakeholder confidence. | Secure domain management interfaces and ensure rapid response to unauthorised changes. |
| Orphaned Domains Due to Departed Registrants | Domains registered to former employees can become difficult to manage or recover. | Administrative challenges, legal issues, and service disruption. | Register domains under the organisation's name and maintain up-to-date contact information. |
| Registrant's Non-Business Domains | Association with compromised personal domains of employees can attract attacks to business domains. | Reputational damage and increased security risk. | Use unique, business-specific contact information for domain registrations. |
| Fake Domains and Unauthorised Transfers | Attackers may register similar domains or transfer existing domains without authorisation. | Brand impersonation, service outages, and data breaches. | Standardise registrant contact information, monitor for similar domains, and apply registrar locks. |
| Unattended Domains | Unused but registered domains can be exploited if they are not actively managed. | Reputational damage, blacklisting, and regulatory fines. | Monitor all registered domains and establish processes for managing unauthorised changes. |
| Unauthorised Domain Transfers | Domains may be transferred without proper authorisation, leading to loss of control. | Service outages, information leakage, and reputational harm. | Apply registrar locks, use unique authorisation codes, and monitor transfer notifications. |
| Stale WHOIS Data | Outdated WHOIS information can facilitate domain hijacking and weaken recovery options. | Service disruption, legal non-compliance, and security vulnerabilities. | Conduct annual WHOIS reviews and maintain evidence of compliance. |
| Inconsistent Domain Registrations | Lack of standardisation in domain information creates management inefficiency. | Increased risk of errors, security gaps, and administrative burden. | Develop and enforce a standard domain management policy covering registration and maintenance. |
| Shared Hosting Vulnerabilities | Hosting services shared with other entities may expose domains to additional risks. | Service outages, information leakage, and reputational damage. | Ensure hosting providers meet security standards and consider dedicated hosting where appropriate. |
| Shared Certificates | Using shared SSL/TLS certificates can undermine customer trust and site authenticity. | Loss of customer confidence and potential data exposure. | Use individual, organisation-validated certificates where identity assurance matters. |
| Use of Let's Encrypt Certificates | Free domain-validated certificates provide encryption but do not prove organisational identity. | Increased risk of phishing and impersonation where users rely on certificates as a trust signal. | Do not treat DV-only certificates as proof of organisational identity; use appropriate organisation-validated certificates where assurance matters. |
| Unreachable WHOIS Contact Email | Inaccessible contact emails can lead to missed warnings or domain suspension. | Service outages and reputational harm. | Use reliable, monitored WHOIS email addresses that are distinct from the domain's own services. |
| Social Engineering Targeting | Personal names in WHOIS records can be exploited for social engineering attacks. | Information leakage and increased susceptibility to attack. | Use organisational or generic contact names in WHOIS records to minimise exposure. |
| Absence of TLS Certificates | Lack of TLS certificates causes browsers to mark sites as insecure. | Loss of customer trust, potential data exposure, and regulatory concern. | Implement TLS and use certificates that provide the level of identity assurance required for the service. |
Practical Principle
Treat domain names like business-critical assets. The question is not only "who bought it?" but "who owns it, who can change it, who monitors it, and what happens if it fails?"